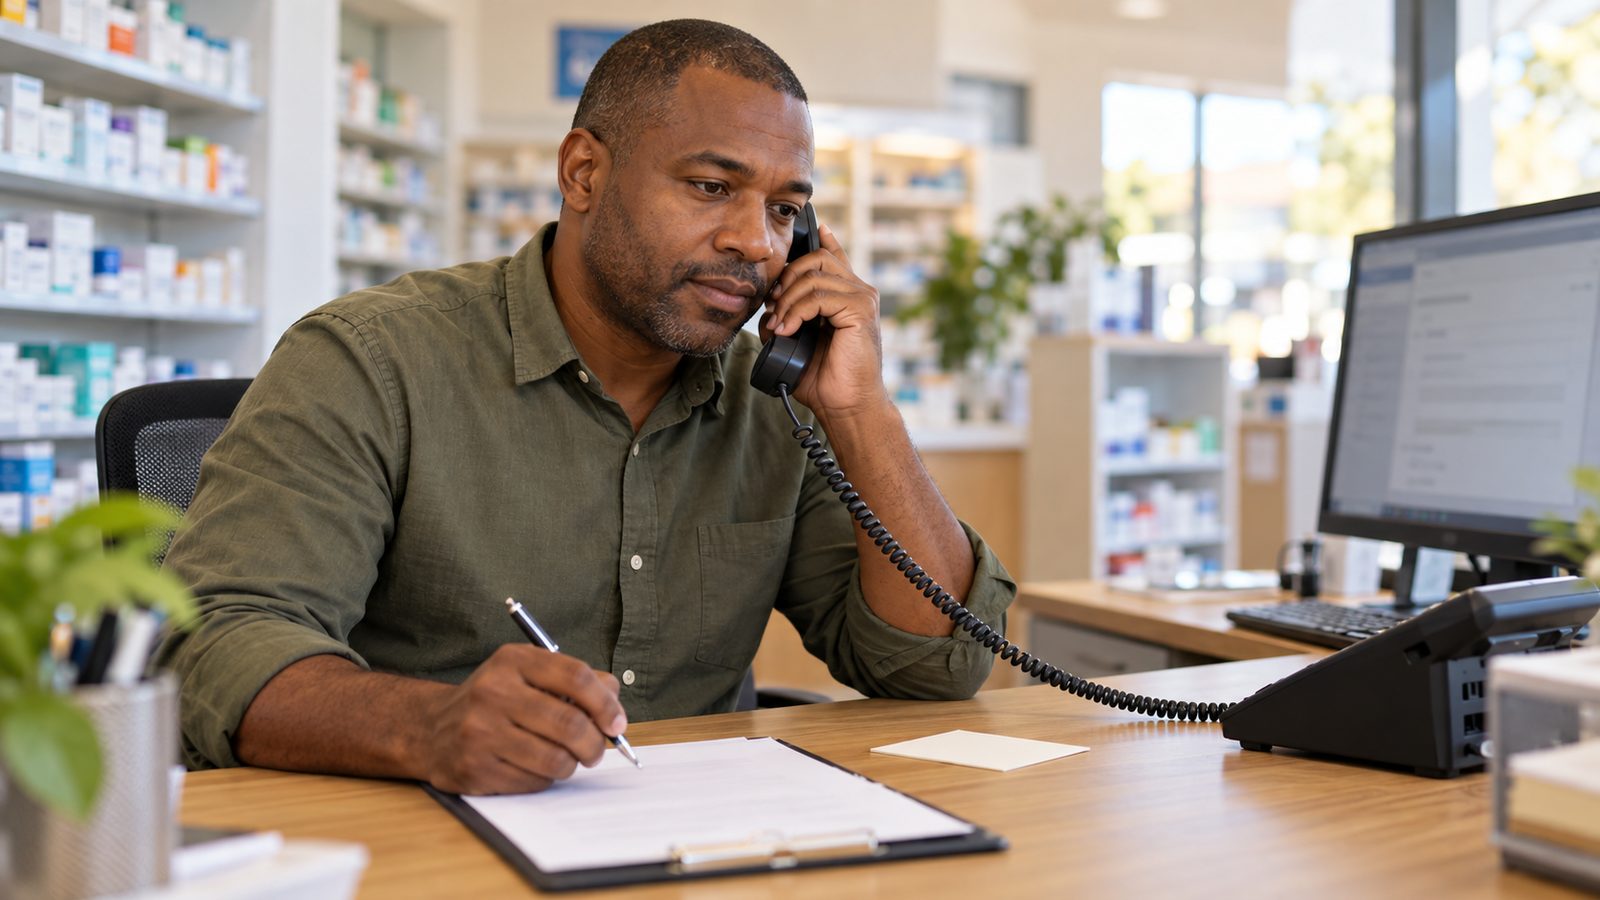
Pharmacy vendor support sessions with a clear finish
Manage a pharmacy vendor support session from independent identity checks to scoped access, supervised work, data handling and verified closure.

Scamwatch recommends checking unexpected contacts through independently sourced details
Source: ScamwatchASD gateway guidance considers approved access methods, supervision and the level of support access
Source: Australian Signals DirectorateOAIC guidance addresses due diligence and personal information controls for third-party providers
Source: OAICIn this article
A pharmacy vendor support session needs an agreed purpose and a clear finish. “The technician has disconnected” may leave questions about access, changes and copied information.
Treat the session as a bounded piece of work. Identify the provider, approve the relevant system, supervise appropriately and verify the closing steps.
This guide covers one support event. Our user access review addresses the separate periodic review of accounts and permissions that remain.
Key facts
- Scamwatch warns about unexpected callers impersonating technical support and recommends independent verification.
- Agree the purpose, access level and pharmacy contact before support starts. Pause if the proposed work moves outside that scope.
- Verify closure and data handling. A completed ticket alone does not establish that temporary access has ended.
Verify the person and the request first
Use an established support portal or trusted contact details to confirm the request. An incoming caller’s knowledge of the pharmacy does not establish their identity.
Check the ticket reference, named provider and expected task through that independent route. If a request is unexpected, stop before opening a remote session or installing software.
Scamwatch’s remote access alert explains how impersonators use familiar screen-sharing tools. It advises against sharing passwords or security codes over the phone.
Keep authentication under the authorised user’s control. Ask the provider for a supported access method rather than reading out a personal password.
The same independent-check habit appears in our supplier payment fraud guide. Here, the decision concerns technical access rather than bank details.
Agree what support may do
Write a short scope in the ticket before connecting. Identify the affected system, observed fault, intended work and pharmacy contact who can approve a change.
Ask whether the provider needs to view the screen, guide a staff member or control the system. Those options should not be treated as interchangeable.
ASD’s gateway operations guidance discusses approved remote access solutions, competent supervision and limiting the level of third-party support access.
That guidance concerns gateway systems, particularly large organisations and government. It informs the questions below; it is not a universal legal checklist for pharmacy software.
| Support proposal | Question before approval | Evidence to retain |
|---|---|---|
| View a configuration | Can staff show the relevant setting only? | Agreed screen or configuration scope |
| Control the workstation | Why is control needed for this fault? | Approver and permitted activities |
| Export a diagnostic file | Does it contain patient or security information? | Reviewed content and approved transfer route |
| Change a setting | What is the impact and recovery approach? | Change description and acceptance check |
| Continue access later | Is a separate approval needed? | Named owner and authorised access period |
Use the provider’s supported change and recovery process. Do not improvise a repair on a live dispensing system because a remote session is already open.
Prepare the workspace and information
Close unrelated windows and remove unnecessary records from view before the session. Decide whether the work should occur outside the busiest service period.
Assign a pharmacy contact who can remain available. If they must leave, agree a pause or handover rather than assuming someone else is watching.
OAIC’s information security guide addresses third-party due diligence, expected controls and contractual handling arrangements. The guide is being updated; check current requirements separately.
Agree how diagnostic files and screenshots will be reviewed and transferred. Prefer a representative test example where it can answer the support question without patient data.
If real information is necessary, obtain the appropriate local approval. Record its purpose and approved destination without placing the contents in a broadly accessible ticket.
Pause when the task changes
Listen for a change from the agreed repair to a wider export, new software installation or additional administrator access. Ask why it is necessary before allowing it.
A useful hypothetical example is a printer fault that expands into a request for the full patient database. That proposal needs a fresh explanation and decision.
Record the decision and who made it. Urgency can affect scheduling, but it does not explain why an unrelated dataset is required.
If the session behaves unexpectedly, follow the pharmacy’s incident arrangements and involve the authorised technical contact. Do not attempt an unfamiliar investigation alone.
Our data breach response guide covers the separate assessment and response process when personal information may have been affected.
Verify the finish before closing the ticket
Ask the provider to summarise changes and any remaining work. Test the agreed outcome using an approved check, then record whether the pharmacy accepted the result.
Confirm the remote connection has ended. Have the authorised administrator verify that temporary access and support functions match the approved continuing configuration.
Check any diagnostic copies against the agreed handling arrangements. ASD’s support guidance discusses contractual data treatment and considering written confirmation of deletion when appropriate.
Do not delete evidence that must be retained for an incident or another obligation. Resolve that question with the responsible owner before asking for disposal.
Record unfinished actions, their owners and the next contact. Keep passwords, recovery codes and unnecessary patient details out of the session record.
The finish is a verified state: the agreed work is recorded, remaining access is understood and someone owns anything unresolved. Then close the support event.
Frequently asked questions
- What should a pharmacy record for a vendor support session?
- Record the verified provider, ticket, approved purpose, system, access method, responsible pharmacy contact, changes, data shared and closure checks.
- Should an unexpected support caller receive remote access?
- Do not grant access on an unexpected caller’s instructions; independently contact the provider through an established trusted route and verify the support request.
- Does closing the helpdesk ticket end remote access?
- Not necessarily. Confirm that the session has ended and temporary permissions or support functions have returned to their approved state.
- Is this a mandatory national pharmacy support procedure?
- No. It is a suggested operational workflow informed by Australian privacy and security guidance; assess system, contractual and legal requirements separately.
Preparation note
Prepared with AI-assisted drafting and primary-source research on 5 November 2026. The example registers and workflows are editorial suggestions, not prescribed national forms.
Publisher: Krepko.
Sources
- Scam alert: Hang up on remote access scammers · National Anti-Scam Centre, Scamwatch · Retrieved
- Gateway security guidance package: Gateway operations and management · Australian Signals Directorate · Retrieved
- Guide to securing personal information · Office of the Australian Information Commissioner · Retrieved